Get Ahead of Hackers with Wazuh – The Ultimate Free SIEM Tool
On this page
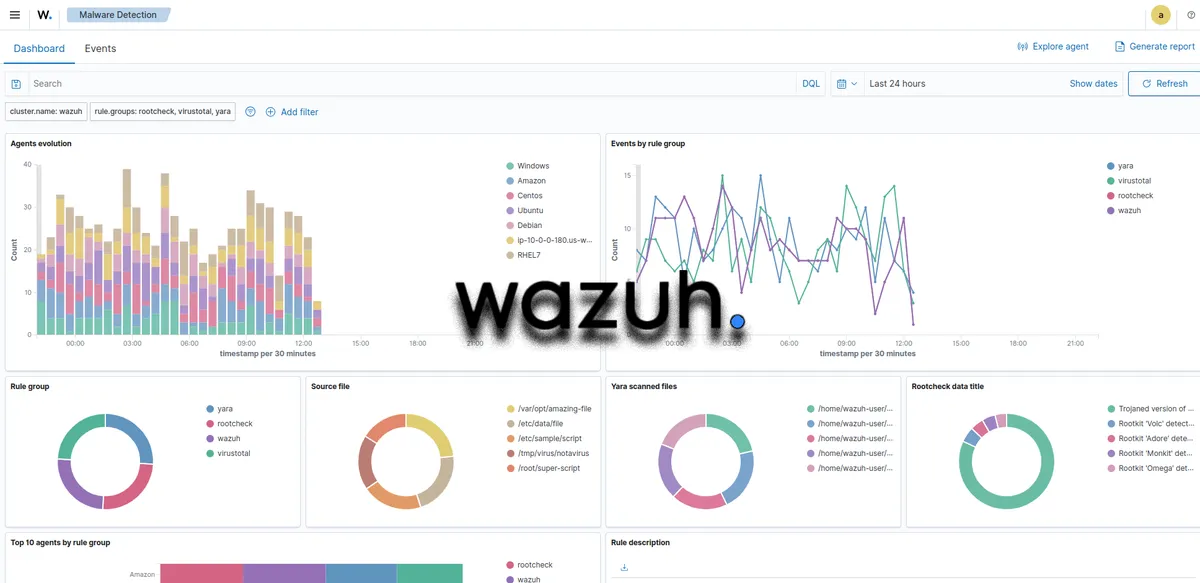
Wazuh is a free, open-source security platform used for threat detection, compliance monitoring, and incident response. It's popular among security professionals because it combines powerful features like SIEM (Security Information and Event Management), host intrusion detection (HIDS), and log analysis—all in one solution.
🧠 Why Use Wazuh?
Wazuh helps organizations:
- Detect threats and suspicious activity in real-time
- Monitor system logs and file changes
- Comply with security standards like PCI DSS, GDPR, HIPAA, etc.
- Respond quickly to security incidents
It’s scalable, integrates well with cloud and on-prem environments, and is perfect for cybersecurity labs, small businesses, and even enterprise use.
⚙️ How Wazuh Works
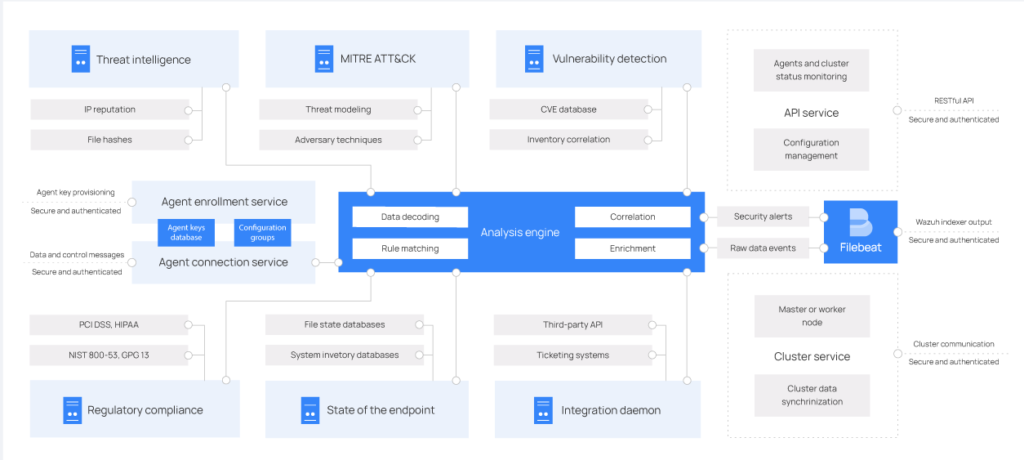
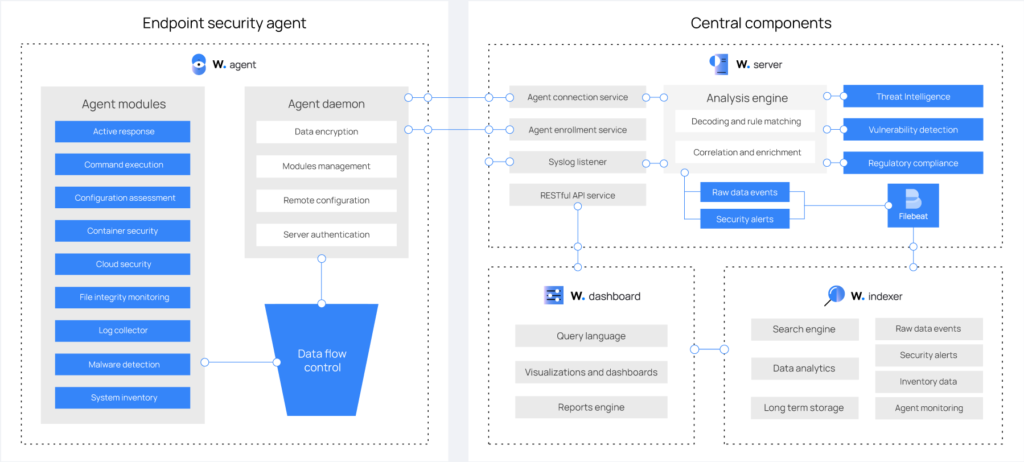
Wazuh has a modular architecture with three main components:
- Wazuh Agent
Installed on endpoints (Linux, Windows, macOS). It monitors logs, file integrity, rootkit detection, etc.
- Wazuh Manager
Central brain that receives data from agents, analyzes it, and generates alerts.
- wazuh indexer/wazuh dashboard
Wazuh works seamlessly with Elasticsearch, Logstash, and Kibana (ELK Stack) for visual dashboards, searching, and analytics.
🛡️ Key Features
- ✅ Log Analysis: Real-time log monitoring with custom rules
- ✅ File Integrity Monitoring: Alerts when key files are changed
- ✅ Intrusion Detection (HIDS): Detect suspicious behavior
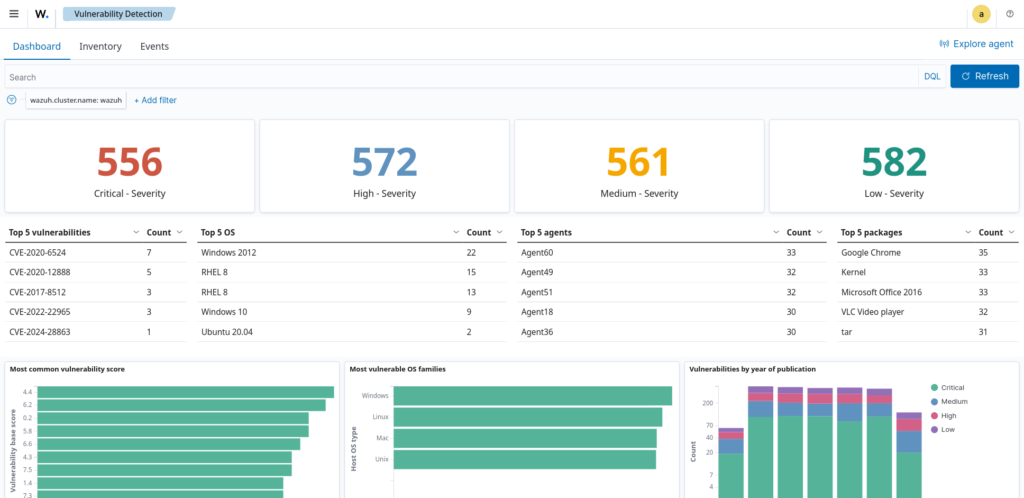
- ✅ Vulnerability Detection: Scans installed packages for known CVEs
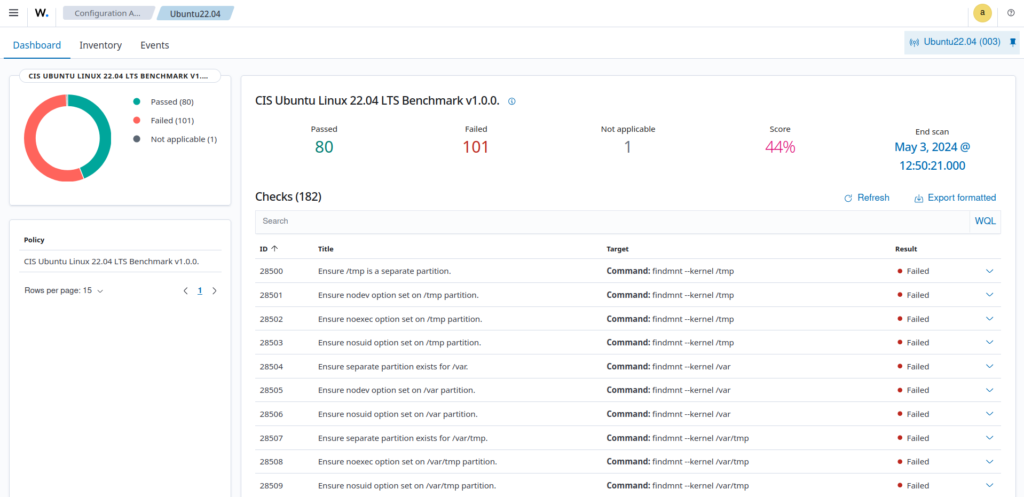
- ✅ Security Configuration Assessment (SCA): Checks system configs against security baselines
- ✅ Active Response: Automatically block IPs or kill processes during attacks
🧪 Wazuh Use Cases
- SOC (Security Operations Center) monitoring
- SIEM integration and log correlation
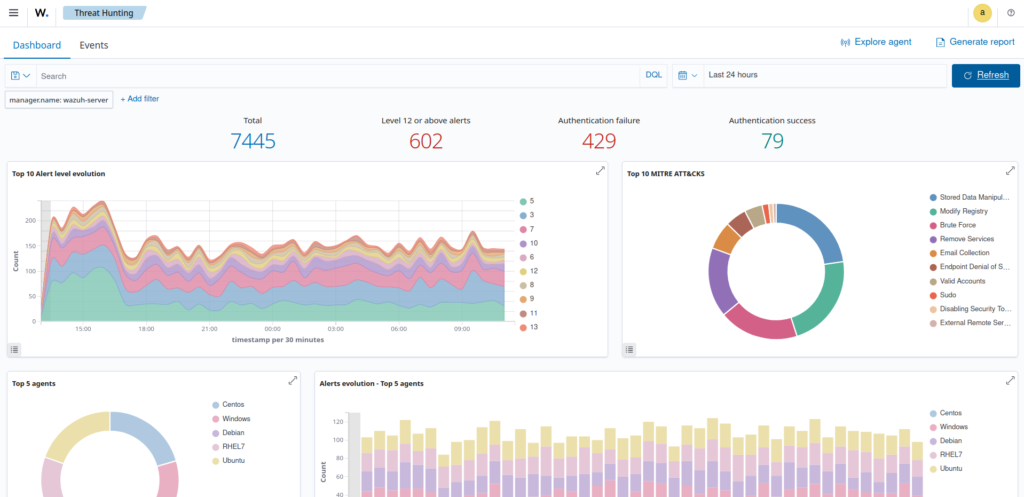
- Threat hunting and forensic analysis
- Cloud security monitoring (AWS, Azure, GCP)
- Compliance enforcement
💻 Who Uses Wazuh?
Wazuh is trusted by:
- Security researchers
- Blue teams
- Penetration testers (for detection avoidance testing)
- DevSecOps teams
- Enterprises needing scalable open-source solutions
🧰 Getting Started
- Install Wazuh using official installation guides
- Set up agents on endpoints
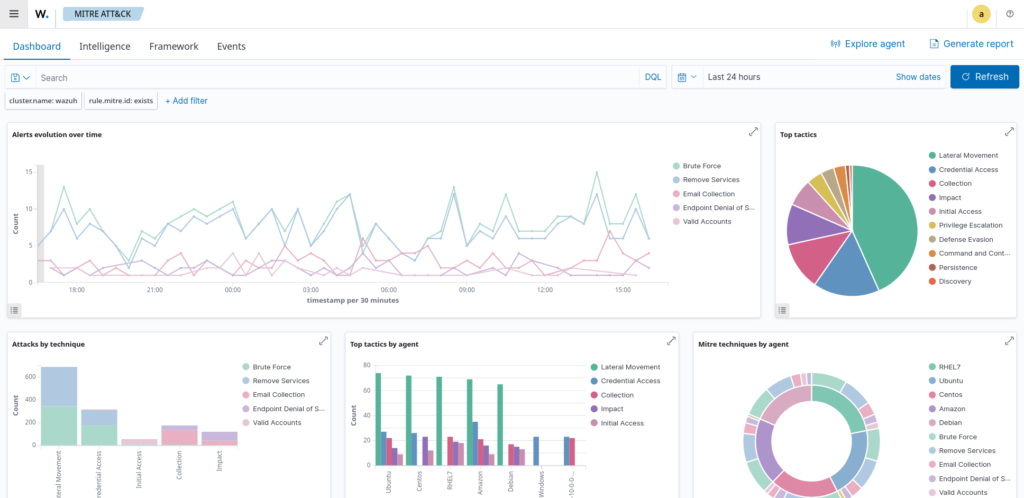
- Use Kibana dashboards for beautiful real-time visualizations